The short version
- A tool call is just an API call with a model choosing the arguments. The entire security question is what credential the call carries — never what the prompt promises.
- Build a thin adapter: tool names and schemas on one side, your existing authenticated API on the other, zero business logic in between. A bug in a thin adapter cannot mint a permission it never held.
- The case study: an MCP server for a production events platform where every tool forwards to the public REST gateway — same scopes, same validation, same rate limits as any API key — and assistant traffic is metered separately so a chatty tool loop is visible.
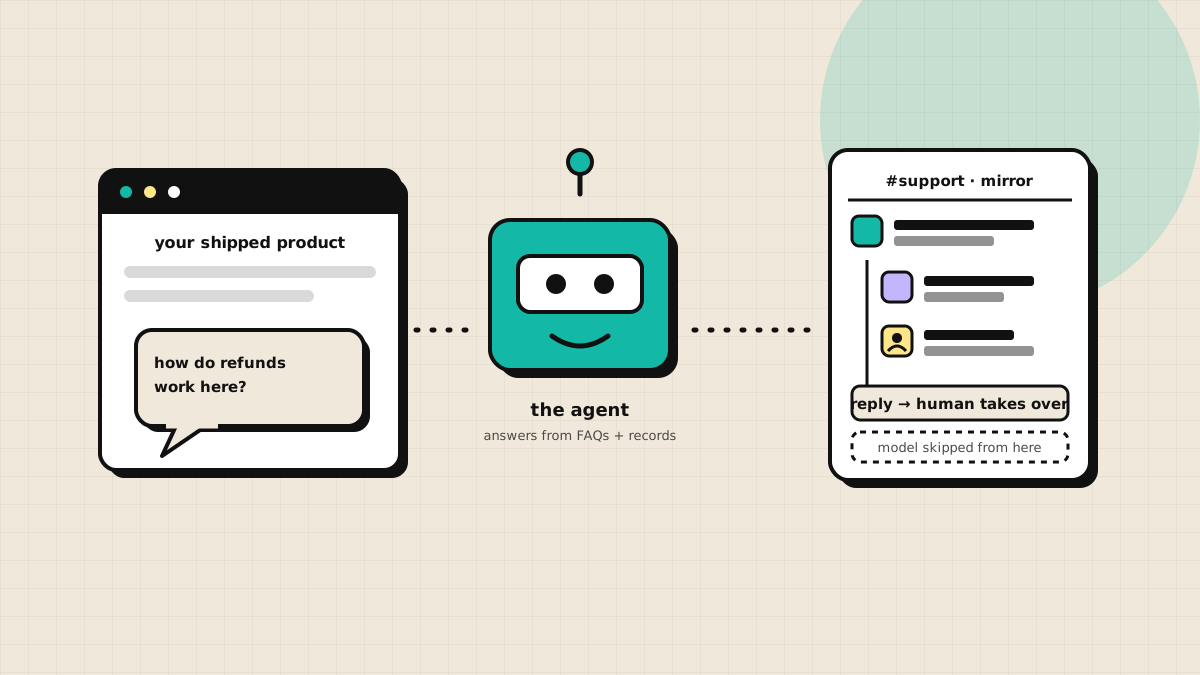
The moment an AI assistant becomes genuinely useful is the moment it stops only talking and starts doing: reading your calendar, creating a draft, querying your product's data. Every one of those actions is the same thing under the hood — the model emitting a structured call to someone's API. Which means connecting agents to tools is not a new discipline; it is API design with a strange new client, one that is eager, tireless, occasionally wrong, and incapable of reading your intentions.
This guide covers how tool calling and MCP work, the architecture that keeps a model-driven client safe, and the production implementation: an MCP server that lets Claude, ChatGPT, and IDE agents operate a live events platform — without getting a single permission its existing API did not already grant.
How tool calling actually works
The mechanics are plainer than the demos suggest. You hand the model a list of tools — name, description, JSON schema of arguments. When the model decides a tool would help, it does not execute anything; it emits a structured request: {"tool": "list_events", "arguments": {...}}. Your code validates that, executes whatever the tool really does, and returns the result as text the model reads before continuing.
Two consequences follow immediately:
- The model never touches your system. Your executor does. Every property you care about — auth, validation, limits — is enforced in the executor, which is ordinary code you control.
- Tool descriptions are prompts. The model chooses tools and fills arguments based on what the descriptions say. Vague descriptions produce wrong calls; your API refusals and rules belong in the descriptions, in the same words your API uses.
MCP (Model Context Protocol) standardizes the plumbing: an MCP server exposes tools in a common format, and any MCP-capable client — Claude, ChatGPT, Cursor, others — can discover and call them. Write the server once instead of one integration per assistant. What MCP deliberately does not provide is your security model. That remains yours.
How you should implement it
Step 1: Make the adapter thin — aggressively thin
The gravitational pull is to make the tool server smart: cache a little, validate a little differently, add a convenience write that combines three API calls. Resist all of it. The correct amount of business logic in a tool adapter is zero: translate tool calls into authenticated requests against your existing API, return the responses, done.
The reasoning is security economics. A thin adapter cannot leak data it never held, cannot bypass validation it does not reimplement, and cannot grant a permission it does not possess — a bug in it produces a failed API call, not a breach. The moment the adapter grows its own logic, it becomes a second backend whose rules can drift from the real one, and every drift is a hole someone finds by accident. If you do not have a public API to forward to yet, build that first — it is the product's takeout counter, and that argument has its own post.
One kitchen, two windows
the kitchen
hundreds of shared pure functions — one recipe per dish, cooked for every caller
the dining room
Our own app. Orders arrive on our own waiters' notepads: callable functions, session auth, UI-shaped payloads.
the takeout counter
The REST gateway. Show some ID, order off a posted menu, get the same food in a box.
- membership cardthe API key
- menu by the windowthe OpenAPI doc
- order numberthe request id
- a line that moves fairlythe rate limit
- standard packagingthe response envelope
Step 2: Let the credential, not the prompt, define capability
The agent's connection authenticates with a real credential — an API key or OAuth grant — carrying explicit scopes. What the agent can do is exactly what that credential can do. Three rules keep this honest:
- Expose discovery tools (
whoami,get_scopes) so the assistant can learn what this connection is instead of guessing. - Never add a "because the AI asked nicely" path. If the scope is missing, the tool fails, and the error should say which scope — readable by the model, actionable by the user.
- Separate reads from writes in scope design, because you will want to grant read-only connections freely and gate writes behind confirmation flows.
Step 3: Design tools for a model, not a developer
A model-facing tool surface differs from an SDK in useful ways. Prefer a few coarse, task-shaped tools over dozens of granular endpoints — models choose better from short menus. Name tools by outcome (create_event, add_tickets) rather than REST anatomy. Put the constraints in the description: what the tool refuses, what must exist first, what it will never accept. And return errors as instructions ("publish requires a description, a location, and a date — ask the user for the missing ones"), because the error text is the model's next prompt.
Step 4: Meter the new client separately
Agent traffic has a unique failure mode: the loop — a model retrying a failing call forever, or enthusiastically enumerating everything. Count tool calls separately from ordinary API-key usage, per tool and per connected app, and keep rate limits on the gateway where they already live. You want "the assistant made 400 calls in an hour" to be a visible fact on a dashboard, not an anomaly you reconstruct from gateway logs.
How I implemented it on a real project
Hosts on the events platform I work on asked the predictable question: can I manage my events from Claude or ChatGPT? The answer became an MCP server with one architectural rule, stated in its README: it holds no business logic and no trust of its own. Every tool is an authenticated request to the platform's public REST API — the same gateway spreadsheet scripts use, with the same keys, scopes, schema validation, and rate limits.
A tool call is just a scoped API call
- The assistant calls a toolClaude, ChatGPT, or an IDE agent invokes list_events, create_event, add_tickets… with plain arguments.
- The MCP adapter forwards itNo business logic, no private database, no trust of its own. The tool call becomes an ordinary authenticated REST request.
- The gateway decidesScopes, schema validation, rate limits, and audit — the same checks every API key already passes. Wrong scope? The tool fails.
- The same backend functions runThe functions the product’s own app calls. There is no second copy of create-event for models to drift away from.
What the tool surface looks like
Reads came first and stayed boring: whoami and get_scopes identify the connection; list_events, get_event, list_guests, get_org return the host's own records, already shaped by the gateway's permission model (guest contact data is a separate scope with its own redaction story). Writes came later and every one is confirmation-gated: create a draft event, publish, add tickets, set a refund policy, close, delete. The bodies are forwarded as-is — the gateway's schemas reject bad input, and the adapter never grew a softer validator than the one the website faces.
Self-serve, not an admin switch
Turning the connector on required no one touching a database flag: a signed-in host opens Developer settings, agrees to the terms, and gets the MCP connector URL plus API-key management — org access limited to owners and admins. Connecting an assistant means pasting the URL and approving the OAuth screen that already existed. If the public API is disabled in an environment, enabling developer settings fails; the assistant cannot route around that, because the assistant is just an API caller.
Instructions as part of the product
The server ships instructions that encode the platform's refusals in plain language: save only what the user said — never invent a description, location, date, or image; resolve relative dates against server time and repeat them back; a live event's refunds can be turned on but never off, and deleting-and-recreating the event to dodge that is explicitly forbidden; settings the tools do not expose are changed in the app, via the one event link. Those sentences exist because models try exactly those workarounds. The tool refuses anyway — the instructions make the refusal legible instead of mysterious.
Usage, split on purpose
The gateway marks calls forwarded from the MCP function so they land in MCP usage totals — per tool, per connected app, with outcomes including rate-limit responses — separate from raw API-key traffic. A chatty tool loop from a chat client shows up as itself, not hidden inside a script's key.
Pitfalls to avoid
- A smart adapter. Every convenience you add to the tool layer is business logic that can drift from the real backend. Forward the call.
- Prompt-level security. "Only access the user's own data" in a description is a wish; the credential's scopes are the control.
- Fifty granular tools. Models mischoose from long menus. Ship task-shaped tools with strong descriptions.
- Opaque errors. A bare 403 teaches the model nothing; an error naming the missing scope or field becomes a correct next step.
- Unmetered agent traffic. If you cannot see tool-call volume per connection, your first loop incident will be a billing surprise.
FAQ
Function calling wires tools into one app you control. MCP standardizes the surface so external assistants — Claude, ChatGPT, IDEs — can connect without per-assistant integrations. If users bring their own assistant, MCP; if you own the only client, either works.
Written by
Rushit Jivani
Senior Software Architect & AI Application Engineer. Architecture that shows up in crash rate, performance and how fast the team ships.